Get Certified in 24–48 Hours.
Fast, Direct, and Accredited.
We help you prepare, audit your systems, and issue your official NCSC-aligned Cyber Essentials, CE+ & IASME Cyber Assurance certificates. No jargon. No complex forms. From £320 + VAT.
Why Choose Us
What Certified UK Businesses Say About SafeWatch
Every Cyber Essentials and Cyber Essentials Plus audit is led directly by our IASME-accredited assessors in Banbury, Oxfordshire. Read verified 5.0-star feedback from UK business leaders on our Official Google Business Profile.
“SafeWatch and Cyber Essentials certification gave our business additional authenticity, and preparing for the audit and the certification process actually helped us think through things differently with new approach.”
“The team at SafeWatch were knowledgeable, approachable and made the whole process much easier to understand. They explained everything clearly, without unnecessary technical jargon, and gave practical advice that made a real difference.”
“Prompt, efficient, and supportive service with a personal approach. Highly recommend.”
“Great service from the Safewatch team. Cyber essentials accreditation and can a time hoover but the guys made it as pain free as possible. I highly recommend.”
Calculate Your Fixed UK SME Certification Fee
Qualify for public-sector, MOD, NHS, and Tier-1 supply-chain tenders with regulated IASME pricing and zero broker commissions.
Includes £25,000 free cyber liability insurance (UK SMEs < £20m turnover) & NCSC v3.3 audit.
- Official IASME Certifying Body • NCSC CE, CE+ & Cyber Assurance (L1/L2)
- UK-based Lead Assessor support (Steven Gordon) — zero call centres
- Need hands-on technical audit? Cyber Essentials Plus from £1,450 + VAT
We Prepare, Create the Assessment, Conduct the Audit & Issue Your Certificate
Because SafeWatch is an official, licensed IASME Certifying Body, you do not need to juggle multiple third-party consultants, brokers, and external audit houses. We deliver the entire certification process in-house from preparation to certificate delivery:
Help You Prepare
We work with your internal IT team or MSP to define your scope boundaries, conduct pre-audit gap diagnostics across the 5 NCSC controls, and provide clear remediation advice to eliminate failure risks before submission.
Create the Official Assessment
As an authorised Certifying Body, we provision and set up your formal organisation account directly on the official IASME assessment platform, registering your declared scope and questionnaire ready for evaluation.
Conduct the Technical Audit
Our accredited Lead Assessors rigorously evaluate your answers and evidence against NCSC v3.3 standards. For Cyber Essentials Plus, we conduct hands-on endpoint auditing and external network vulnerability scans.
Issue the Official Certificate
Upon audit sign-off, SafeWatch directly signs and issues your official UK Cyber Essentials or Plus certificate, registers your organisation on the NCSC National Database, and activates your £25,000 free cyber liability insurance.
Official IASME Certifying Body
Licensed directly by IASME and NCSC, SafeWatch replaces reseller markups and call-centre queues with direct Banbury-based Principal Assessor accountability:
- Official IASME Banded Fees: Statutory pricing from £320 + VAT with zero consultant or broker commission added on top.
- Named Lead Assessor Access: Direct telephone and scoping guidance from Steven Gordon (07920 151412) throughout your audit.
- Full Accreditation Suite Under One Roof: Certified delivery across Cyber Essentials, Cyber Essentials Plus, and IASME Cyber Assurance (Level 1 & 2).
- Commercial Tender & Insurer Alignment: Formatted to pass PPN 09/14 public procurement, MOD/NHS supply-chain checks, and activate automatic cyber liability cover.
Continuous Cyber Essentials Compliance Retainer
Stop treating Cyber Essentials as an annual compliance scramble. Whenever you onboard cloud tools, deploy new laptops, or adjust firewall rules, your scope shifts. Our 365-day retainer gives you year-round direct access to Lead Assessor Steven Gordon, quarterly checks, and your annual certification included.
Watch: Cyber Essentials — Implementing the Firewalls Control
Learn how to satisfy the 5 mandatory NCSC v3.3 boundary firewall requirements, cloud security groups, and remote worker router scoping in this 90-second Lead Assessor guide.
UK Government Mandates Cyber Essentials Across Supply Chains (£90M Package)
The UK Government has announced a landmark £90 million national resilience package to establish Cyber Essentials as the non-negotiable security baseline across UK supply chains and critical sectors. Backed by the new Cyber Resilience Pledge and tightened procurement rules, organisations must demonstrate compliance to win public and enterprise contracts. As an accredited Certifying Body, SafeWatch helps businesses audit perimeters, implement MFA, and achieve certified status.
Cyber Essentials Requirements Checklist: The 5 Controls
Use this as your Cyber Essentials checklist. SafeWatch audits organisations against the five core technical requirements specified under the latest NCSC standard:
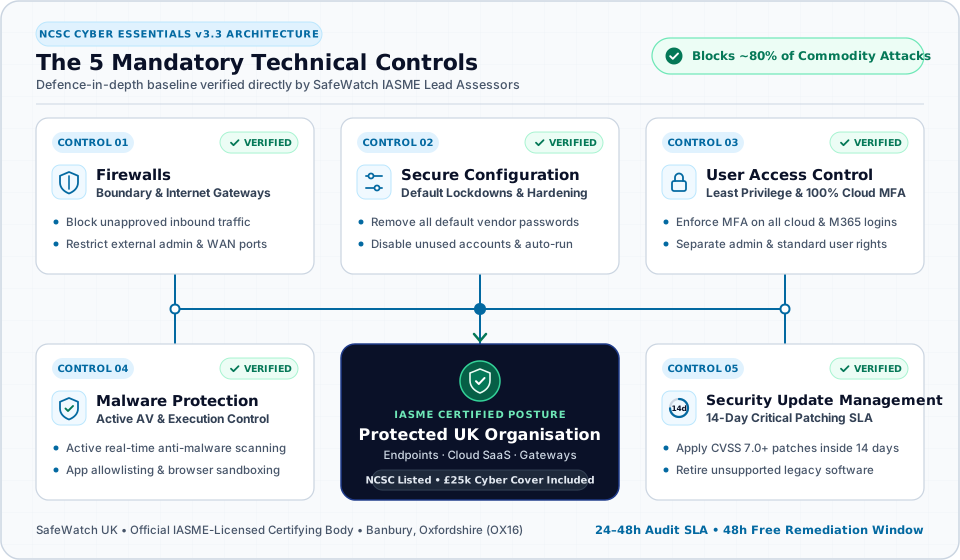
Enforce strict corporate firewall perimeters to protect all internal network segments, WAN gateways, and subnets. Any open ports or misconfigured router access lists represent immediate vulnerabilities and will result in automatic audit failure. Read full Boundary Firewalls guide →
Eliminate security drift by enforcing corporate templates that disable default manufacturer accounts, enforce complex custom logins, shut down unnecessary auto-run properties, and lock down active protocols. Read full Secure Configuration guide →
Limit administrative accounts strictly to those who need them and enforce least privilege. Under the current NCSC Cyber Essentials standard (Willow / Danzell), Multi-Factor Authentication (MFA) must be active on 100% of user and admin logins across cloud services (SaaS/PaaS/IaaS) holding business data. Read full User Access & MFA guide →
Protect organisational systems against malicious code. Audits verify that all endpoints run active anti-malware software, utilise application sandboxing, and configure strict code signing to block untrusted applications. Read full Malware Defence guide →
Establish strict administrative policies ensuring all operating systems, software packages, and firewalls are patched within 14 days of a critical or high-risk vulnerability release, mitigating zero-day exploits. Read full 14-Day Patch SLA guide →
Frequently Asked Questions
Clear, practical answers from our Banbury-based IASME Lead Assessors on achieving UK Cyber Essentials certification.
Yes. Because SafeWatch is an accredited IASME Certifying Body licensed by the NCSC, we deliver the complete certification lifecycle in-house—from pre-submission gap review and IASME portal setup through to technical audit (including hands-on verification for CE+) and official certificate issuance with automatic £25,000 cyber cover (eligible UK SMEs under £20m turnover).
This direct model removes reseller delays and commissions, with statutory IASME fees from £320 + VAT and direct access to Lead Assessor Steven Gordon on 07920 151412.
Cyber Essentials is the UK government-backed certification scheme designed to block up to 80% of common internet-borne cyber attacks (NCSC research). Guided directly by our UK-based IASME Lead Assessors, SafeWatch manages your scoping review, technical verification, and official sign-off. Review the technical scope on the official NCSC Cyber Essentials standards, or preview the official IASME Cyber Essentials question set.
SafeWatch aligns school and academy trust networks with UK Department for Education (DfE) Digital Standards and Risk Protection Arrangement (RPA) conditions. Our IASME Lead Assessors guide school IT teams through segmenting pupil Wi-Fi subnets, locking down BYOD access, and achieving official certification.
Yes, under Procurement Policy Note PPN 09/14, any supplier bidding for UK central government contracts that involve handling personal, sensitive, or public data must hold a valid Cyber Essentials certification.
The official Cyber Essentials requirements and framework standards are published directly by the UK National Cyber Security Centre. You can access the complete overview and download the technical infrastructure guidelines on the official NCSC Cyber Essentials standards page.
You can download the latest official Cyber Essentials self-assessment questions for preparation. Simply visit the IASME Cyber Essentials Question Set Download page to retrieve the current requirements document in PDF or Excel formats.
SafeWatch (safe-watch.co.uk) is an accredited UK Cyber Essentials Certifying Body licensed by IASME and the NCSC. We are a professional cybersecurity auditing and compliance advisory service. SafeWatch does not produce, distribute, or require downloadable consumer executable software such as safewatch.exe. If you find a file named safewatch.exe on a personal computer, it is unrelated third-party software or adware and should be examined with standard antivirus tools.
Are you a Midlands MSP? Partner with SafeWatch
Managed Service Providers (MSPs) across Oxfordshire, Warwickshire, and the Midlands partner with SafeWatch for independent compliance auditing without commercial conflict. We do not sell IT support or managed services—your client relationships remain protected while we audit and you deliver the remediation upgrades.